Skip to content

External Data Protection Officer · DACH · companies up to 100 employees

Data protection,
clearly regulated.

One fixed contact person, one system for documentation, contracts, training and deadlines. Plus AI, website and automation, built GDPR-compliant from the start.

Free first call
Modern office with glass walls

Role

Appointed data protection officer under Art. 37 GDPR and § 38 BDSG

For whom

Companies up to 100 employees in the DACH region, German and English

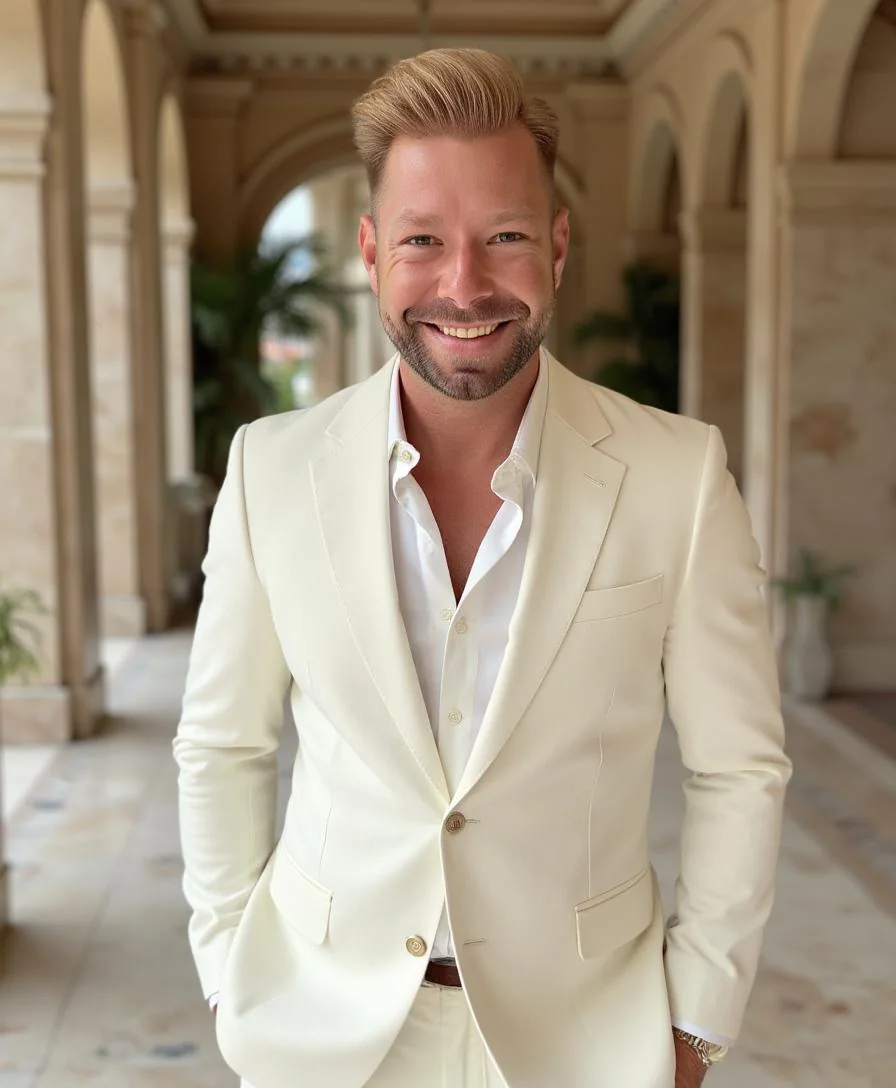
Kai Tobias Mispelbaum

Your contact

Kai Tobias Mispelbaum

Reply within two working days

External Data Protection Officer · Art. 37 GDPR · § 38 BDSG · Records Art. 30 · Data processing agreements Art. 28 · Training with records · Deletion deadlines · AI policy · Website without cookie banner · Reply within two working days · 

Our standard

Data protection needs a partner who is reachable and forgets nothing.

Personal advice and a system that reminds you of records, contracts, training and deletion deadlines by itself. Evidence is there when someone asks.

0fixed contact person
0working days response time
0steps, always the same
Office meeting, legal framework GDPR and BDSG

Legal framework

GDPR · BDSG · TDDDG · EU AI Act · Art. 28 DPA · Art. 30 records

Sound familiar?

The supervisory authority writes, and nobody knows where the records are. A customer requests access, the clock is running. Your team types customer data into ChatGPT. And in the end, management is liable. Personally.

For most companies up to 100 employees, data protection is a binder nobody has opened since 2018. Until it blows up. We take over the role, the deadlines and the documentation, so you run your business again instead of paragraphs.

Three areas

From one source.
In one order.

The external data protection officer is the foundation. AI, website and automation build on it and are designed so that data protection is in from the start.

Office meeting

01 · Foundation

External
Data Protection Officer

Appointed under Art. 37 GDPR and § 38 BDSG. Advice, monitoring, training, contact with the supervisory authority. Monthly, with fixed availability and documentation in one place.

What is included
Open-plan office

02 · Build

AI in your
company

Tool selection, AI policy, staff training, your own AI systems. Legal basis, data processing agreements and documentation are part of the blueprint, not rework.

Learn more
Workstations in the office

03 · Operations

Website and
automation

Your website calls no third parties, no cookie banner needed. Records, contracts, training and deletion deadlines are maintained with system support and remind by themselves.

Learn more

What you never chase again

Three things that
otherwise stick to you.

Signed GDPR documents, records of processing activities
01

Records · Art. 30

  • Processing activities
  • Data processing agreements, Art. 28
  • Technical and organisational measures
  • Deletion concept
  • Policies

When the authority asks

Records, contracts, measures: in place, current, presentable within an hour. Not after three weeks of searching.

Data protection consultant on the phone, quick query in the office
02

When a question comes up

New tool, new vendor, customer wants access? You ask instead of guessing. Reply within two working days.

Employees in a data protection training session at a flipchart
03

When an employee makes the mistake

Trained, documented, repeated. The mistake stays an isolated case, not your liability.

Deadlines that report themselves.

Four things that get forgotten in daily business when nobody looks. With us they live in one system and remind in time. The evidence is created along the way.

Shelf full of binders, symbolising the records of processing activities
Art. 30

Records of processing activities

continuously maintained, changes reminded

Signing a data processing agreement
Art. 28

Data processing agreements

reviewed per vendor, expiry reminded

Team in a data protection training session, proof of staff training
Training

Training deadlines

who was trained when, when the refresher is due

Calendar for deletion deadlines, when personal data must be deleted
Deletion

Deletion deadlines

which data has to go when, with a log

How it works

Five steps. Always in this order.

Every project, whether data protection, AI, website or automation, follows the same pattern. You always know where we stand and what comes next.

01

Analysis

Inventory: processing activities, systems, vendors, contracts, documents. Result: status report with gap list.

02

Objectives

What must be met, what makes sense, what comes first. Agreed with management. Result: target picture with priorities.

03

Planning

Measures, owners, dates, effort. Result: action plan with dates.

04

Implementation

Records, contracts, measures, deletion concept, training, website, AI processes. We implement, you approve. Result: documentation that exists.

05

Control

Ongoing review, training records, incident logs, annual report. Result: evidence for authority and customers. Then the cycle starts again.

Why companies switch

Personal. Digital. From one source.

A person, not an inbox. You talk to the person responsible for your data protection. No rotating consultants, no anonymous support team.

Contact person

One system for all deadlines. Records, contracts, training and deletion deadlines remind by themselves. A fixed monthly fee instead of hourly billing.

System and costs

Meeting at a table, AI, website and automation from one source

Whoever is responsible for data protection should be able to build what affects it. AI rollout, website and process automation come from the same hand.

More than data protection

Working together

Three ways. A fixed monthly fee instead of hourly billing.

Analysis

One-off

Inventory with gap list and priorities.

  • · Inventory of all processing activities and vendors
  • · Review of existing documents
  • · Target picture and action plan
Enquire

External Data Protection Officer

Monthly

Appointment, ongoing support, documentation, training, deadlines.

  • · Official appointment under Art. 37 GDPR
  • · Fixed contact person, reply within two working days
  • · Records, contracts, training, deletion deadlines in the system
  • · Incident management and annual report
First call

Projects

By effort

AI rollout, website, automation, built GDPR-compliant.

  • · AI policy, tool assessment, custom systems
  • · Website without cookie banner
  • · Automation of the DPO process
Enquire

We name the exact fee in the first call, depending on company size, processing activities and vendors.

Frequently asked

Good to know.

Not covered? Write to info@soulution.systems, reply within two working days.

Advises management and staff, monitors compliance, assists with data protection impact assessments, is the point of contact for data subjects and cooperates with the supervisory authority (Art. 39 GDPR). In practice this includes maintaining the mandatory documents: records, vendor contracts, technical and organisational measures, deletion concept.

In Germany, as soon as at least 20 persons are regularly and permanently engaged in automated processing of personal data (§ 38 (1) BDSG). Regardless of headcount, the duty can apply when processing requires a data protection impact assessment or data is processed commercially for transfer. Below the threshold all other GDPR duties still apply.

An internal DPO ties up working time, needs ongoing training and, if the appointment is mandatory, enjoys special dismissal protection (§ 6 (4) BDSG). An external DPO brings expertise and tools, costs a fixed monthly fee and can be ended with the contract. For companies up to 100 employees the external option is usually the more economical one.

We take them over. During the analysis we review existing records, contracts, policies and training records, check them for currency and transfer them into the system. Nothing is done twice.

Maintenance of the records of processing activities and of data processing agreements, including reminders on expiry or change. Plus tracking of training and deletion deadlines. The evidence is created automatically.

The legal entity is Soulution Enterprise LLP, based in Canada. The service is offered exclusively to companies in the DACH region, in German or English. Data protection matters reach us at dsgvo@soulution.systems.

Glass facade of an office building

Free first call · 30 minutes

Let us start
with clarity.

You describe where you stand. We tell you whether you need a data protection officer, how the service works and what it costs. No obligation, no preparation.

Kai Tobias Mispelbaum

Kai Tobias Mispelbaum

Founder, owner, data protection officer Soulution.Systems